The Cyber Industry Built Our Defenses Roof First.
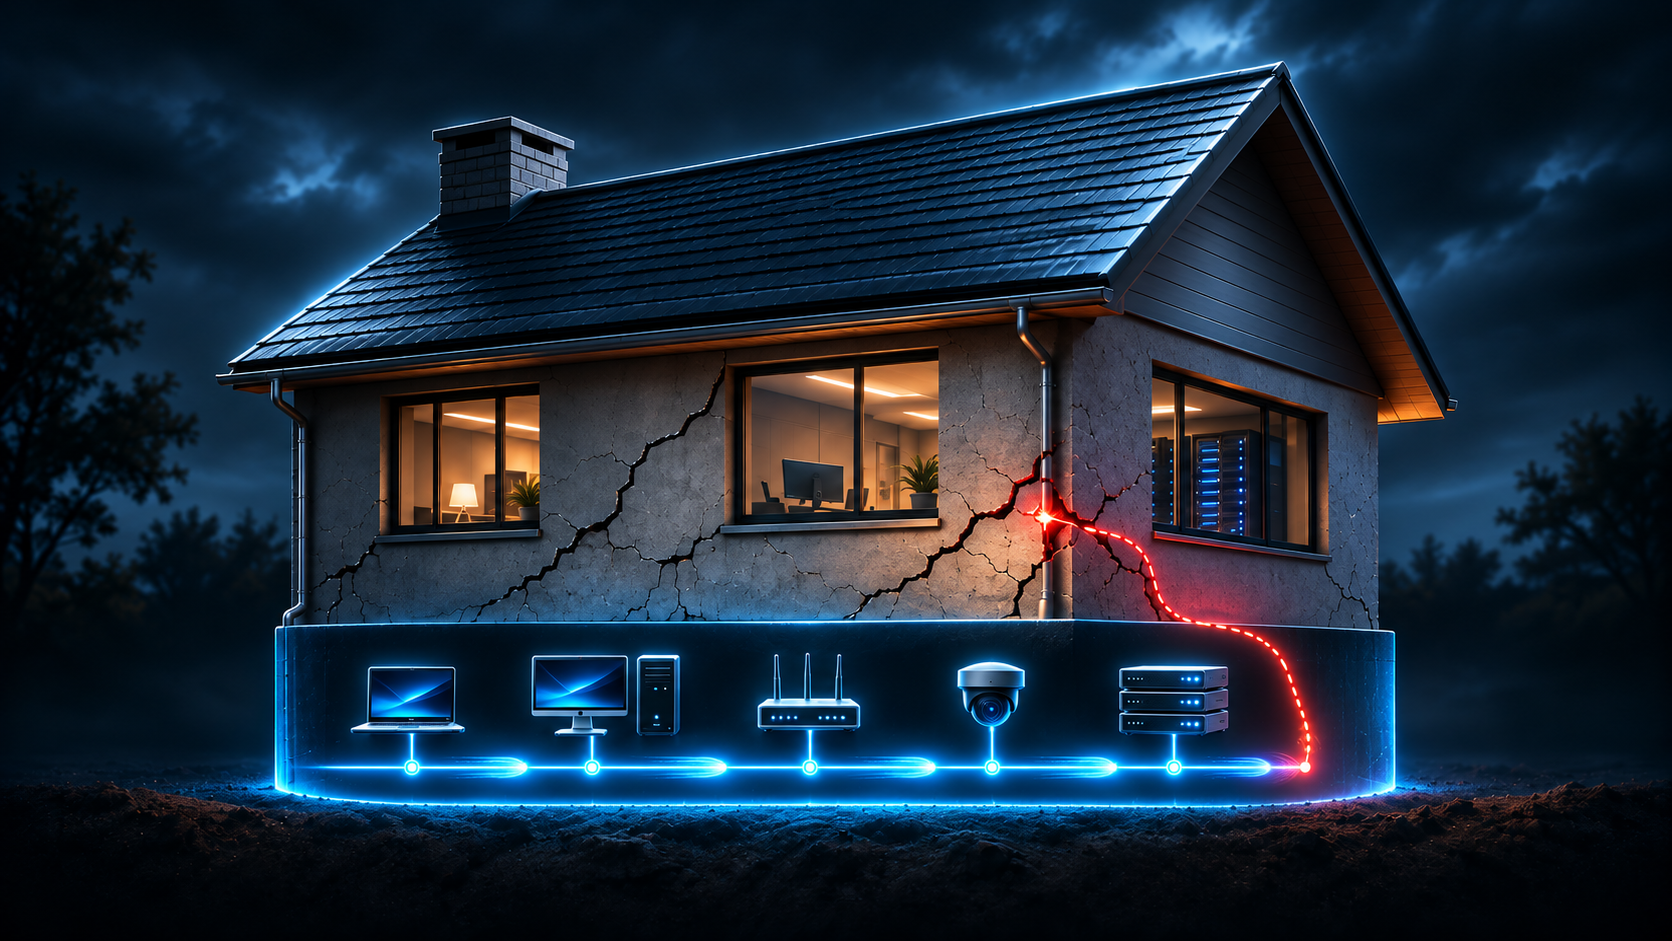
And now we wonder why the walls keep cracking.
The network is the foundation. It’s how the devices and systems your business depends on communicate.
What’s connected to yours right now?
What can each device reach?
How many of those paths does the business actually need?
Too often, our industry skips that last question. We’ve invested heavily in tools that tell us when a connection looks suspicious, yet we leave open paths the business never needed.
Every unnecessary path is a gift to the attacker. Once an attacker controls one device, automation lets them search for the next target while your team is still reading the first alert. Every path you close in advance is one less race you have to win.
That’s why Ridgeback Network Defense begins at Layer 2, where devices connect to the local network.
→ Know the ground. See what’s actually connected, including equipment missing from your inventory.
→ Hold the ground. Decide which devices belong. Ridgeback can automatically isolate an unauthorized device when it joins.
→ Defend the ground. A device that belongs can still fall under an attacker’s control. When it starts searching for its next target, unassigned addresses answer as Phantom assets (there is nothing there, except from the perspective of the offending machine). At first contact with a Phantom, Ridgeback can isolate the probing device under a rule you set in advance, without waiting for an analyst to determine intent.
Build endpoint protection, identity controls and behavioral analysis on that foundation. You can make better use of all three once you know what’s connected, what belongs and what each device should be able to reach.
If one device on your network were compromised tonight, what could it reach simply because nobody ever decided it shouldn’t?